
Zero Trust Network Access (ZTNA): complete security for every access
In a world where mobility and remote working are everywhere, WANUP takes an advanced Zero Trust approach, guaranteeing watertight network security. The principle is simple: trust no device attempting to connect from outside our physical or virtual appliances.
With this approach, any device not recognised as belonging to the customer’s LAN or WAN is automatically subjected to an advanced encrypted tunnelling system. This mechanism relies on the latest technologies on the market and forces every external connection (remote working, mobility) to pass through a secure platform hosted in France (Cloud SAYSE). We have named this system “always on” to underline that security is always “on”, whatever device is trying to connect and wherever it is.
Secure, controlled remote access.
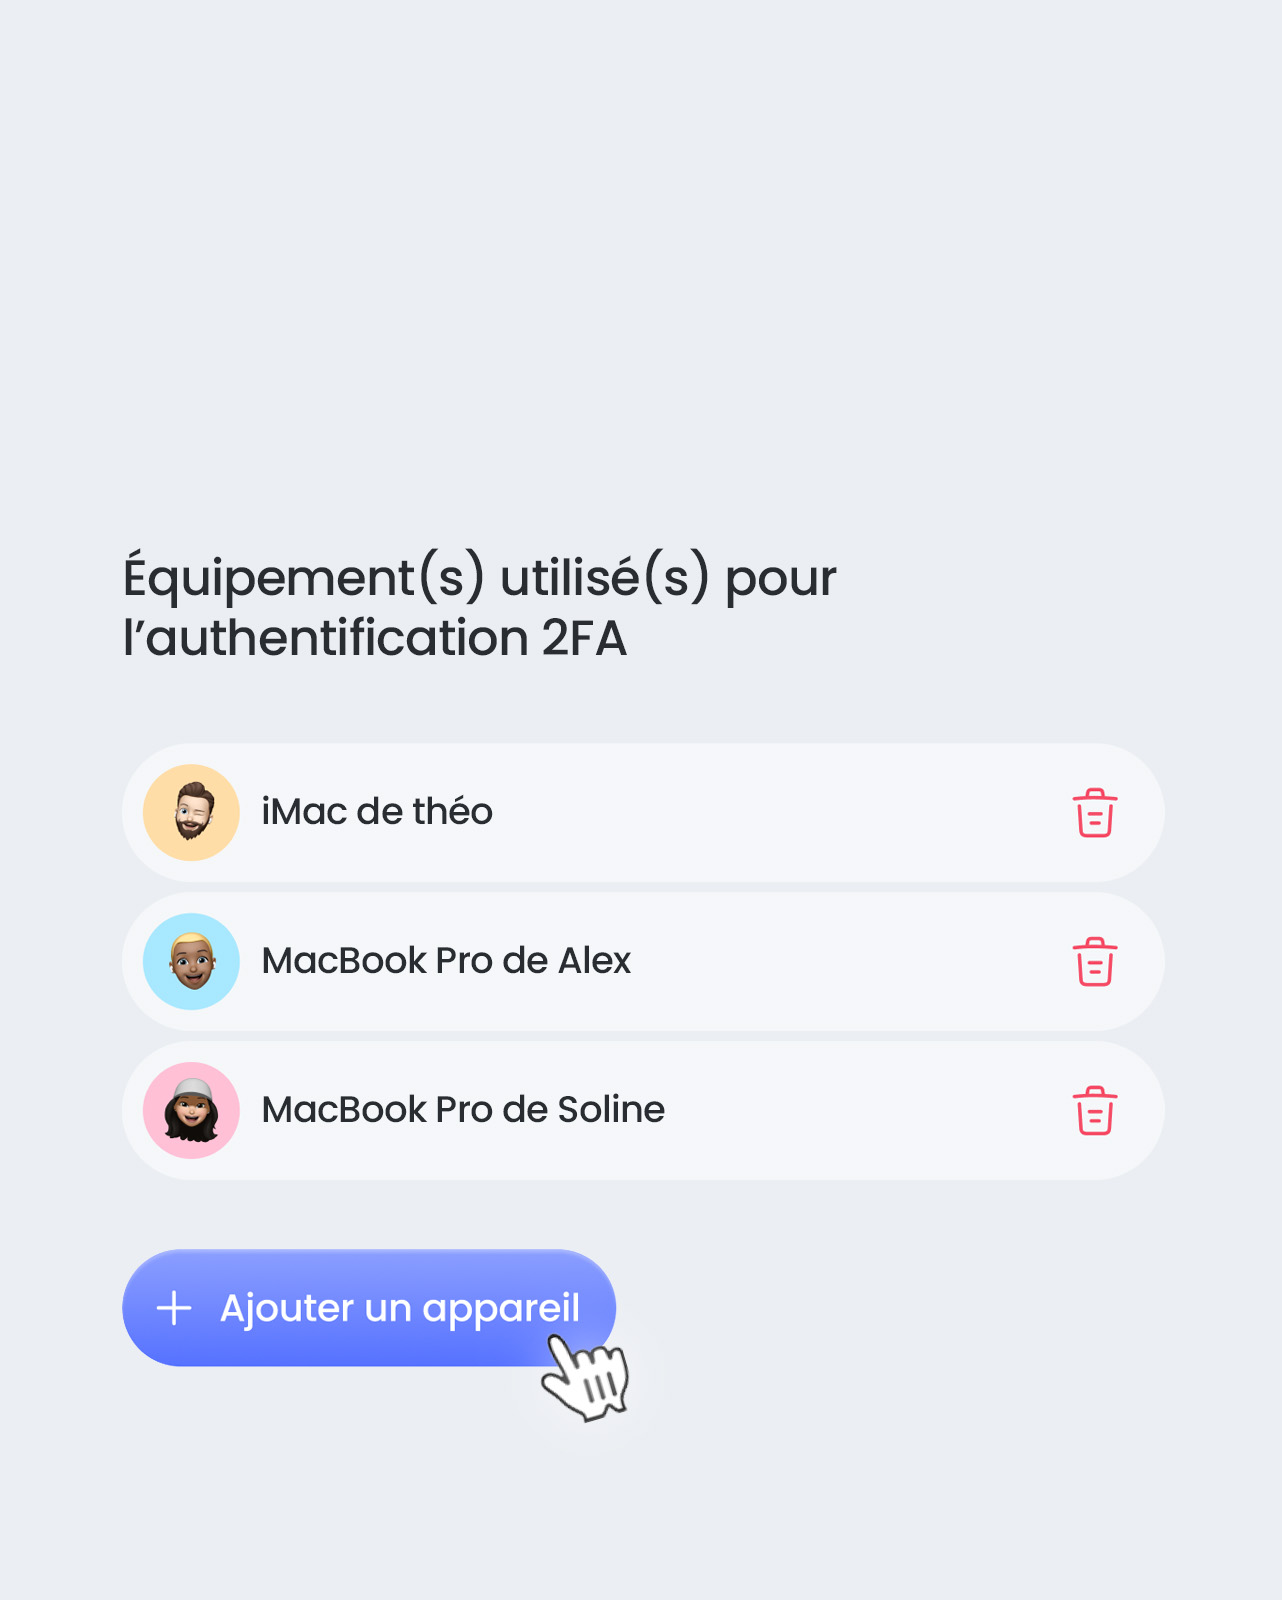
Strong authentication.
No access is granted without strict verification of identity and device, applying the “Zero Trust” principle.

Encrypted tunnelling.
Automatic set-up of a secure tunnel based on cutting-edge encryption technologies to encapsulate and protect traffic.

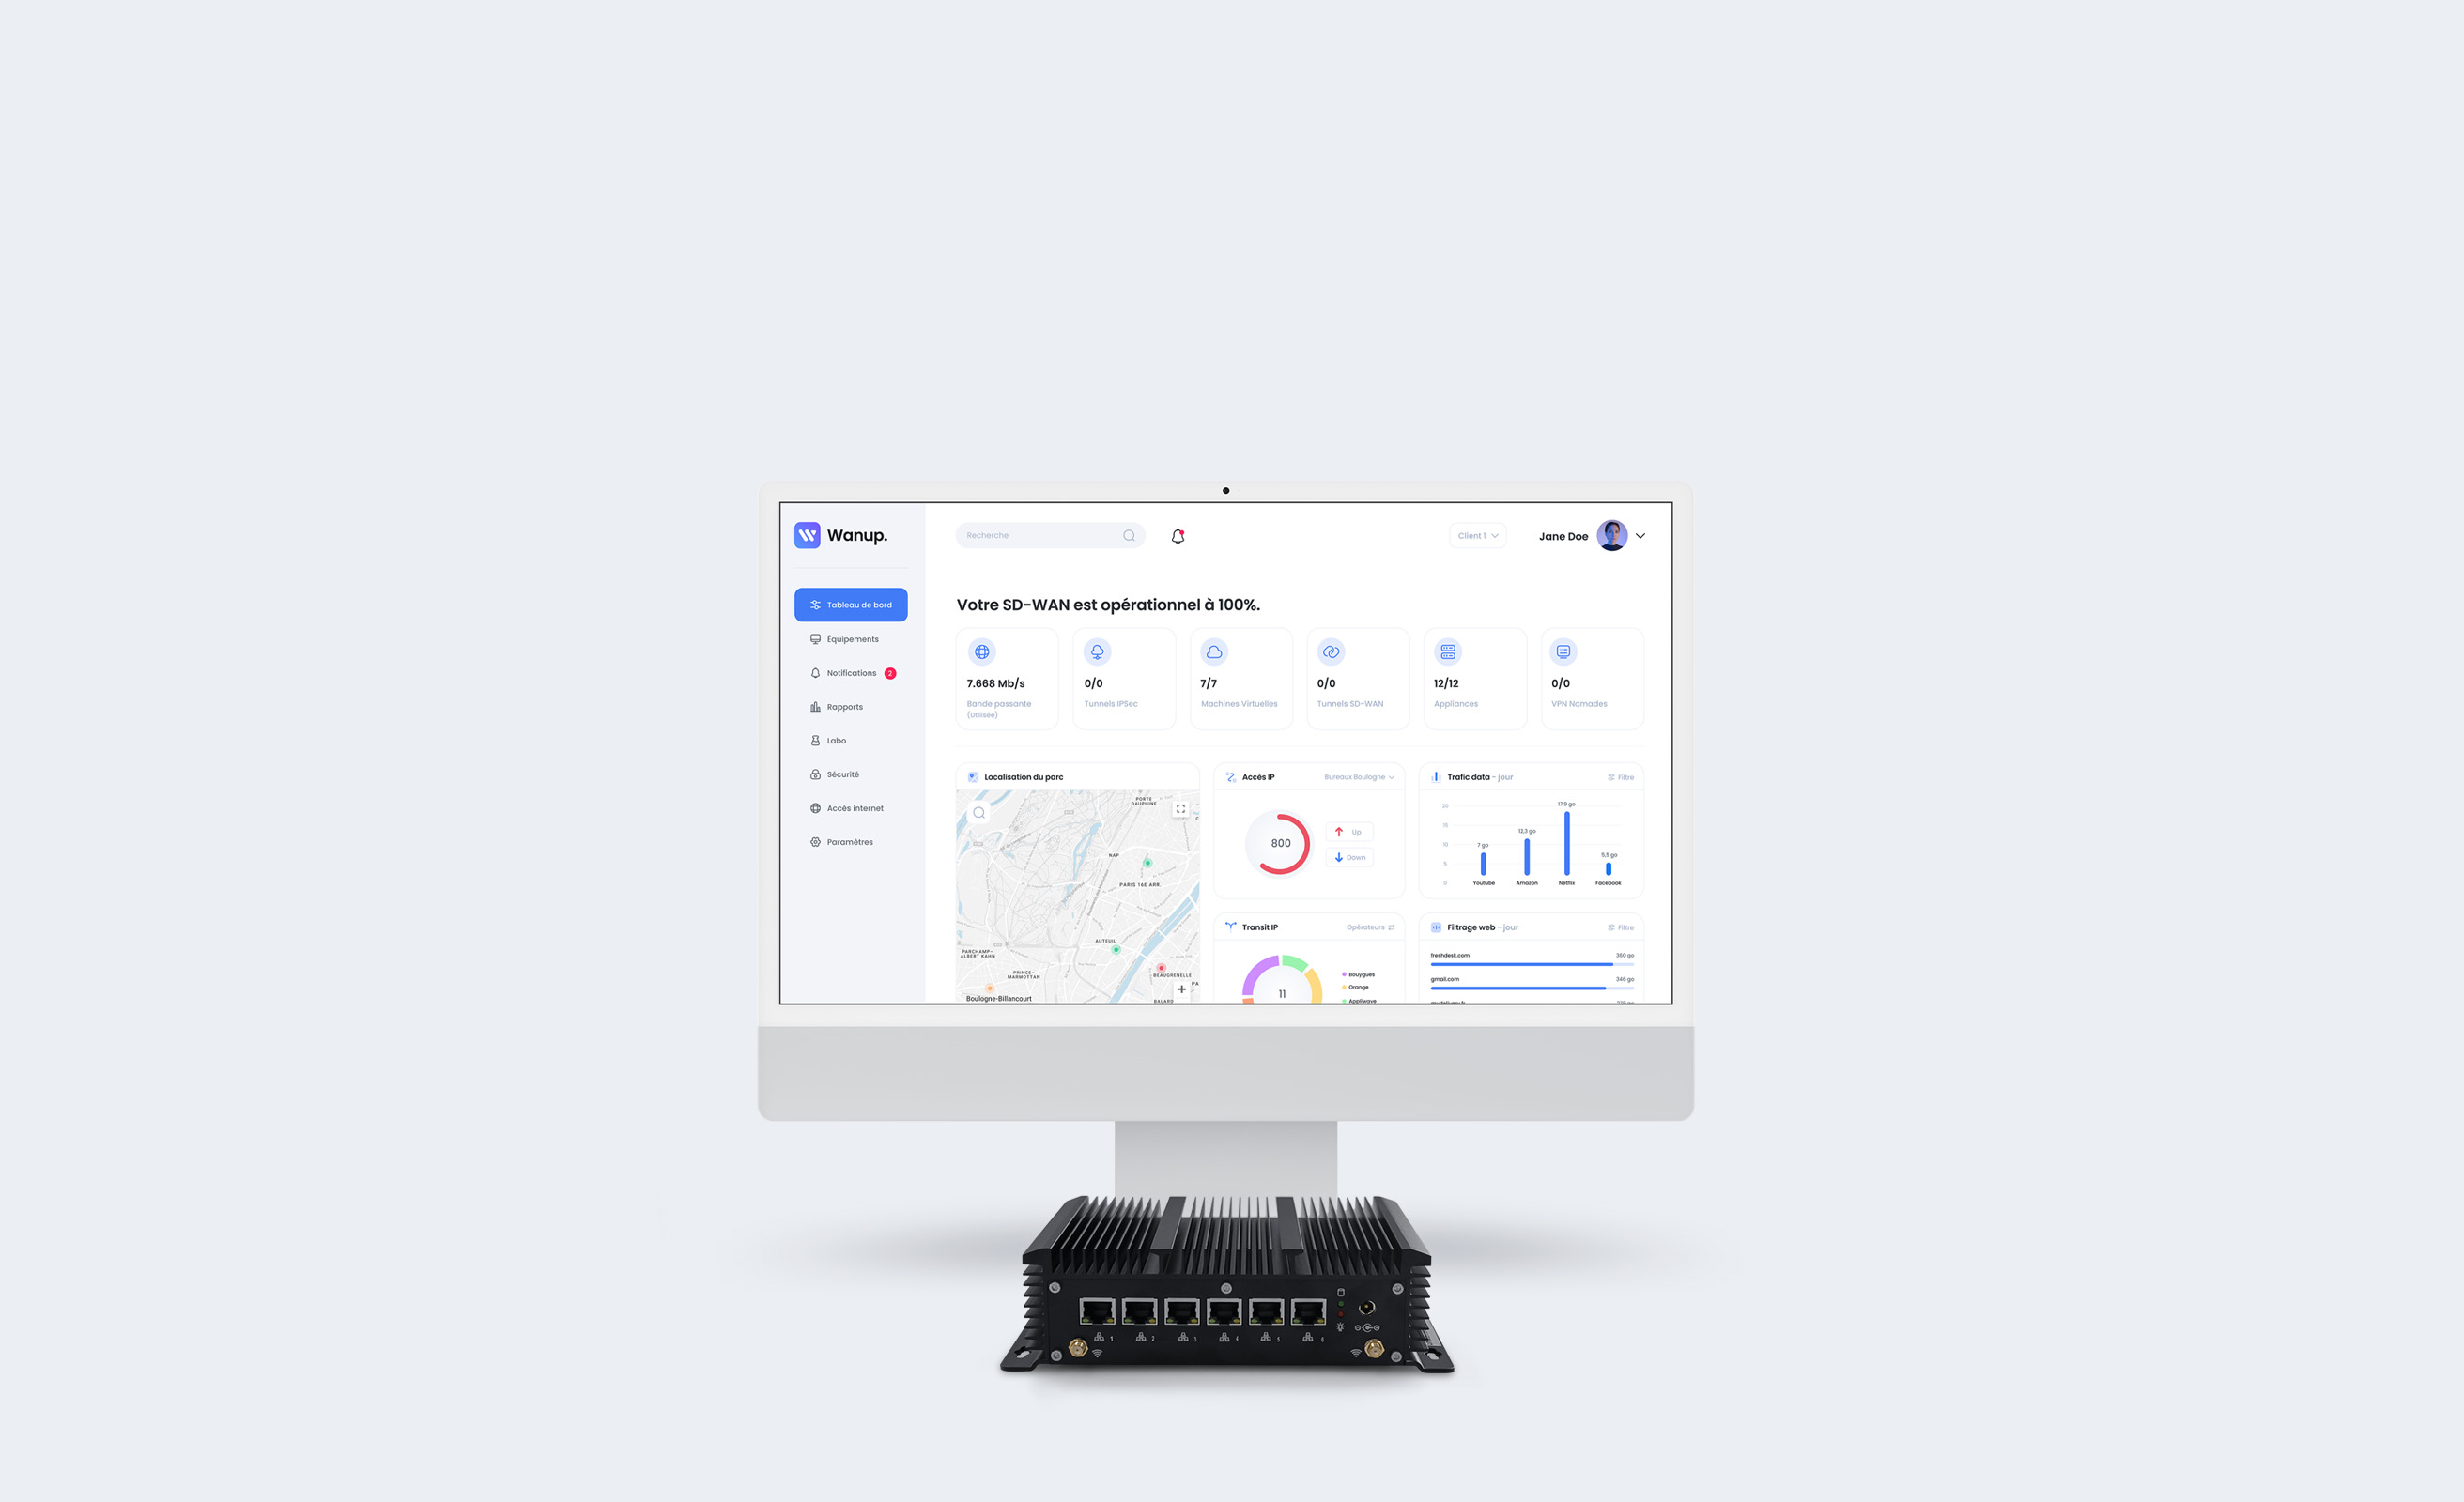
Native integration with Wanup.
The entire system is managed directly from our Wanup interface, simplifying administration and ensuring full consistency with each customer’s SASE policies.
Controlled, segmented access.
Connections are segmented, preventing any lateral movement by a potential attacker and restricting access to authorised resources only.
Consistent security.
Wherever it is, every workstation is secured in the same way, ensuring uniform protection for both office-based and mobile users.

Security and performance without compromise: with WANUP, Zero Trust Network Access becomes a tangible reality.
No connection is left to chance, guaranteeing optimal protection without compromising network fluidity.
Customer case studies
Discover how our solution
is implemented in the field.


